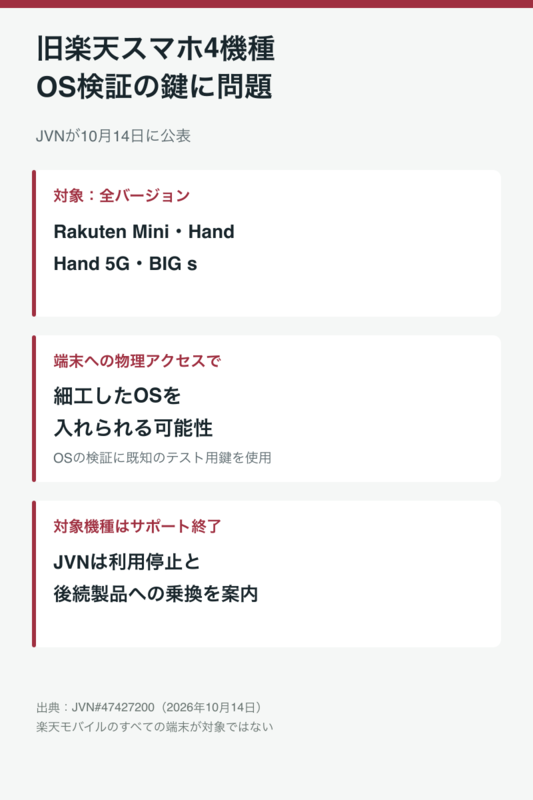
JVN, which publishes vulnerability information, announced on October 14th that a problem has been identified in the mechanism for verifying OS tampering at startup in four Rakuten Mobile smartphone models. The affected models include all versions of Rakuten Mini, Rakuten Hand, Rakuten Hand 5G, and Rakuten BIG s. Physical access to the device could potentially allow a manipulated OS to be installed.
The issue lies within a mechanism called "Android Verified Boot (AVB)," which checks whether the OS or other components have been tampered with during Android startup. Normally, verification is performed using keys managed by the device manufacturer. However, in the affected models, a known test key, originally prepared for Android development, was used as is.
An attacker with physical access to the device could potentially install a manipulated system image. As all four models have reached end-of-support, users are advised to avoid continued use and switch to other products.
Made with AI