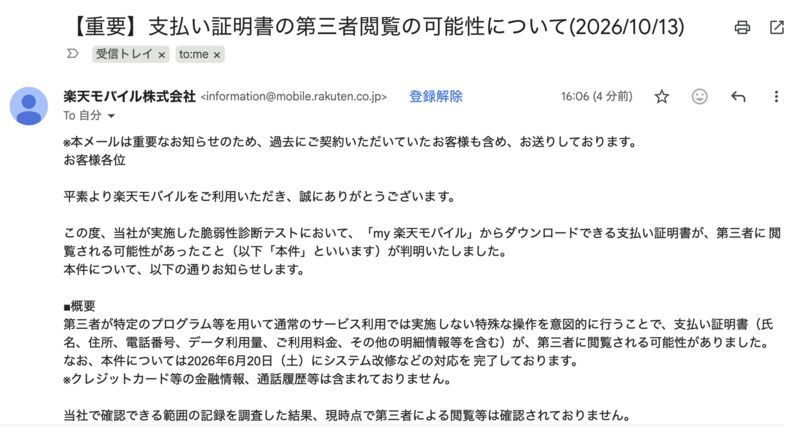
Rakuten Mobile sent an email notification to its users on October 13, stating that payment certificates downloadable from "my Rakuten Mobile" could have been viewed by a third party. This potentially exposed usage fees and personal information to unauthorized individuals. The notification also applies to users who previously held contracts with the company.
The vulnerability was discovered during a security assessment test conducted by Rakuten Mobile. It was found that a third party could potentially view other users' payment certificates by intentionally executing specific, non-standard operations using certain programs, which are not part of normal service usage.
The payment certificates contain information such as name, address, phone number, data usage, usage fees, and other detailed billing information. However, they do not include financial information like credit card details or call history.
Rakuten Mobile completed system modifications and other countermeasures by June 20, 2026. After investigating records within the scope the company can confirm, no third-party viewing has been confirmed to date, nor have any related secondary damages been identified. The company also stated that it has already reported the incident to the relevant authorities.