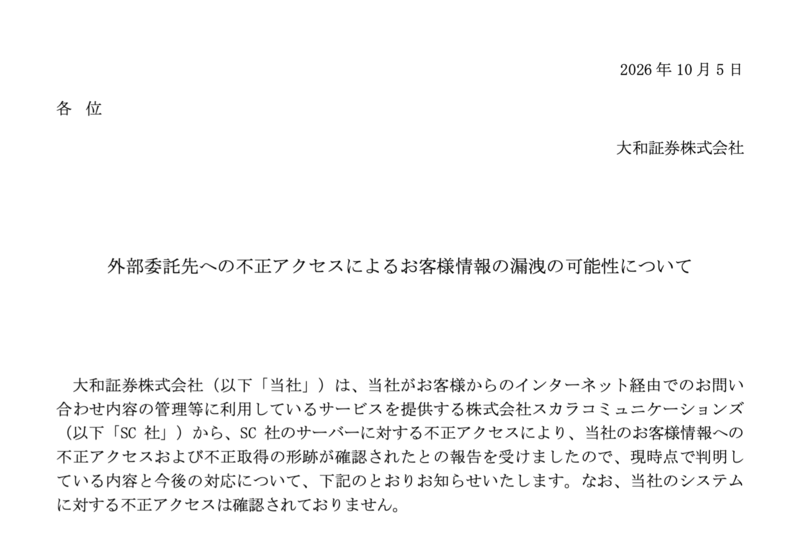
Daiwa Securities announced on October 5th that its external contractor, Scala Communications (SC Co.), experienced unauthorized access, potentially leading to the illicit acquisition of customer information stored on SC Co.'s servers. The unauthorized access occurred between approximately 8:33 PM on October 2nd and 8:01 AM on October 3rd.
Daiwa Securities utilized SC Co.'s services for managing inquiries received via the internet, among other functions. The potentially leaked information includes names, email addresses, and account numbers for approximately 110,000 individuals. When including inquiry details that do not identify individuals, the total number of affected items reaches approximately 220,000.
The attack specifically targeted SC Co.'s servers, and no unauthorized access to Daiwa Securities' own systems has been confirmed. The company states that the potentially leaked information alone is insufficient to access securities accounts or conduct transactions. As of October 5th, no unauthorized transactions or public disclosure/dissemination of the information on the internet have been confirmed.
Daiwa Securities plans to individually contact all affected customers. The company is also issuing a warning, advising customers to be vigilant against potential phishing emails or phone calls impersonating Daiwa Securities, which might exploit names and inquiry details. Customers are urged not to provide sensitive information such as transaction IDs, passwords, PINs, or one-time passwords.