Incidents of credit card information theft, perpetrated by tampering with e-commerce site payment screens to steal entered data, are occurring in rapid succession.
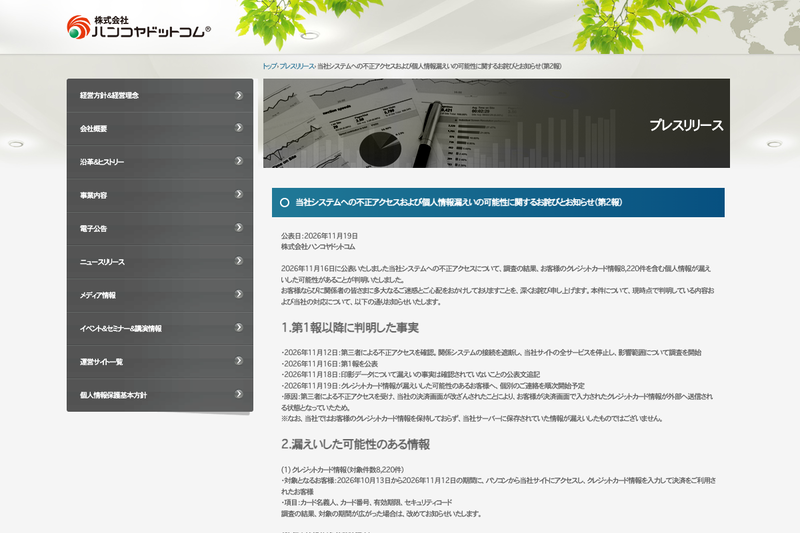
On November 19, Hankoya Dot Com announced the potential leakage of personal information, including 8,220 credit card details. The previous day, November 18, confectionery maker Rokkatei also disclosed the potential leakage of approximately 8,000 credit card details from its online store.
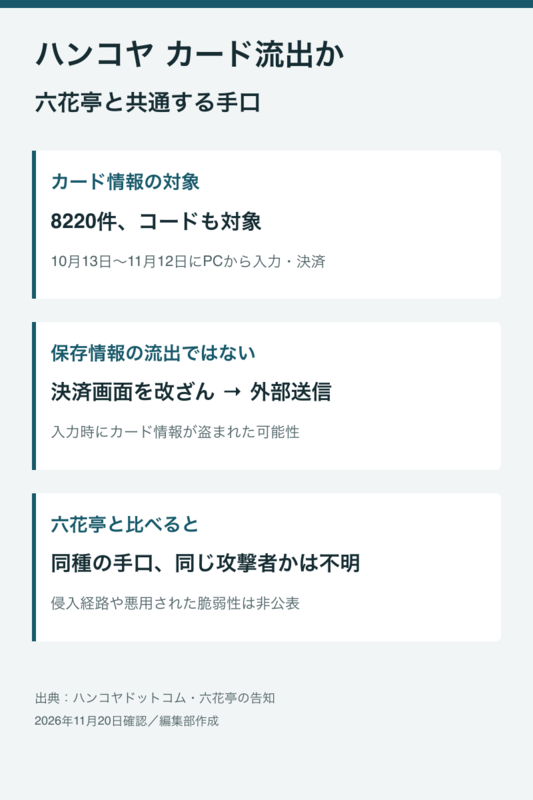
Common to both companies is the method of tampering with online store payment screens to transmit card information entered by users to an external party. Even if card information is not stored on the server, it can be stolen the moment it is entered. Both companies reported that not only card numbers and expiration dates but also security codes may have been leaked.
For Hankoya Dot Com, those affected by the credit card information leak are users who accessed the site from a PC and made card payments between October 13 and November 12. For customers who registered as members or placed orders on the site, personal details such as names, addresses, phone numbers, email addresses, login IDs, and hashed passwords may also have been leaked.
At Rokkatei, users who entered card information on the online store between October 21 and November 18 are affected. While there are many commonalities in the incidents affecting both companies, it is not yet known if they were carried out by the same attacker.
Both companies are proceeding with individual notifications to affected parties and are urging users to check their card statements and contact their card company if they find any unfamiliar charges.
When the payment screen itself is tampered with, it is difficult for users to notice any anomaly based on appearance alone. As this can happen even on frequently used e-commerce sites, it is advisable to regularly check your credit card statements.
Made with AI