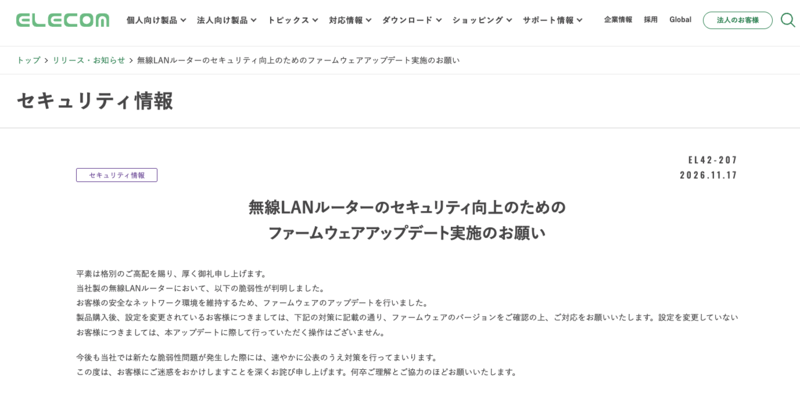
Elecom has announced a firmware update to address security vulnerabilities in its wireless LAN routers: WRC-BE36QS-B, WRC-BE36QSD-B, and WRC-W701-B. Existing users are advised to check their firmware version, depending on whether they have modified their settings, and update if necessary.
The newly identified vulnerability could allow an attacker who gains access and logs into the settings screen to execute arbitrary commands. This vulnerability is categorized as CVE-2026-101113, and Elecom is urging users to apply firmware Ver. 2.2.3 or later as the patched version. Users who have not altered their factory default settings will not require any additional action, as the firmware automatically updates.
The affected products are the three models: WRC-BE36QS-B, WRC-BE36QSD-B, and WRC-W701-B. Users who have changed their settings or have concerns should visit the guidance page to confirm their firmware version and perform the update.
Elecom pledges to promptly disclose and implement countermeasures for any new vulnerabilities discovered in the future. To maintain a secure network environment, it is crucial for users of the affected devices to regularly check their update status.