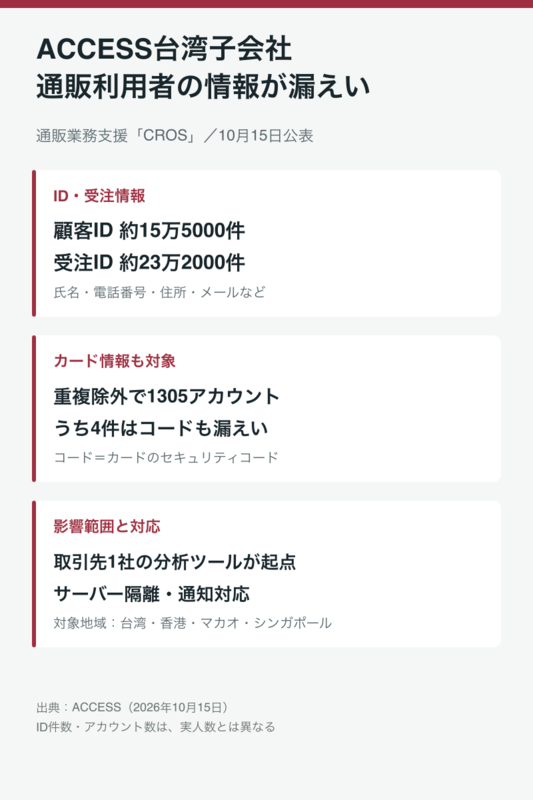
The compromised ID-related items include names, phone numbers, addresses, email addresses, and associated order information, affecting users in Taiwan, Hong Kong, Macau, and Singapore. The 1,305 credit card records represent the number of unique accounts after consolidating duplicate registrations. This information pertained to orders for which payment had not yet been completed.
For four of these accounts, all items, including card numbers, security codes, and expiration dates, were leaked. For the remaining 1,301 accounts, information other than the security code was compromised. Furthermore, using key information for an email sending service stolen from the compromised server, 11,441 fraudulent emails were also sent. The company believes that the recipient list used for sending these emails is separate from the leaked personal information.
Made with AI