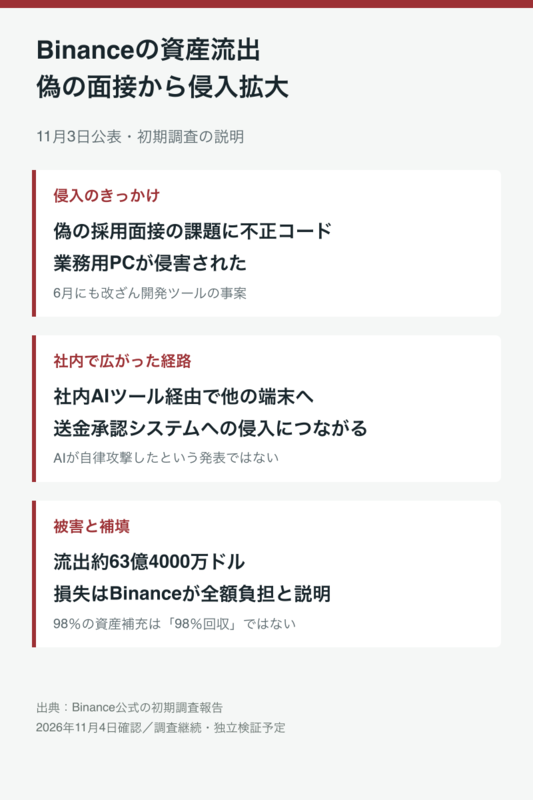
On November 3rd, cryptocurrency exchange Binance announced the initial findings of an incident involving the outflow of crypto assets worth $6.34 billion. The company stated that the system for approving asset transfers was exploited through a combination of intrusions via fake job interviews, tampered development tools, and internal AI tools.
According to Binance, in June 2026, a wallet development and operations engineer, attempting to install an AI coding tool, downloaded a tampered Homebrew installer. Although the issue was addressed by replacing the device and changing credentials, information about the engineer's duties and colleagues was already known to the attackers.
In September, another software engineer was contacted by a fake recruiter through a legitimate job service. The attackers gained trust through video interviews and then instructed the engineer to download a programming challenge to their work PC. The challenge contained malicious code, which, according to the report, could not be detected by the device protection tools at the time.
On October 20th, the attackers infiltrated the devices of two wallet engineers from the compromised PC via an internal AI tool. They discovered credentials that allowed them to deploy containers (execution environments), which led to the intrusion into the system that approves transfers on October 30th.
Stopping the asset outflow also proved difficult. The attackers had set up permissions on the blockchain that allowed them to bypass normal withdrawal procedures. Even when Binance halted withdrawals, the pre-configured permissions were not automatically invalidated. The company stated that in addition to stopping transfers, it was necessary to revoke the illicit permissions.
Made with AI