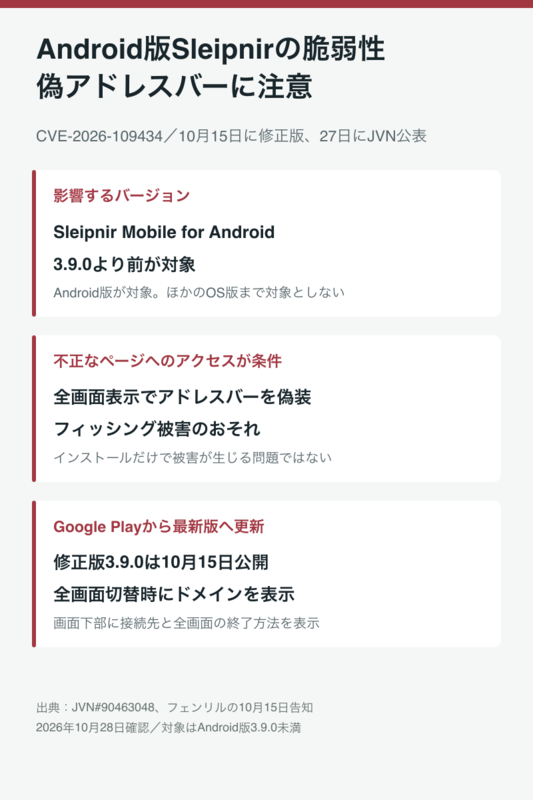
On October 27, JVN announced a vulnerability in Fenrir's web browser, "Sleipnir Mobile for Android," that could display fake address bars and other elements. Versions prior to 3.9.0 are affected.
The issue allowed for the spoofing of address bars and other indicators of the accessed site by exploiting the full-screen display feature. If users trust the displayed information, they might not realize they are accessing a different site than intended, potentially falling victim to phishing scams or similar attacks.
Fenrir released the patched version 3.9.0 on October 15. The specification has been changed to display the currently accessed domain name and instructions on how to exit full-screen mode at the bottom of the screen when switching to full-screen display. Users on older versions are advised to update to the latest version.
Made with AI