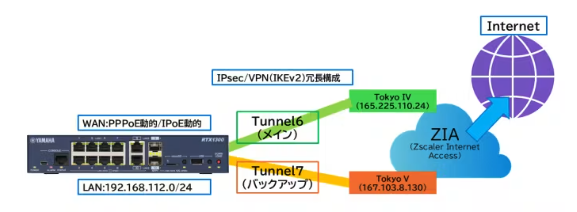
An IPsec connection configuration example has been released for utilizing the cloud security service "Zscaler Internet Access (ZIA)" with the Yamaha router "RTX1300." This example is based on connection verification results by SCSK Corporation, with the verified model being the RTX1300 Rev.23.00.17 and the target cloud being Zscaler Cloud "zscalerthree.net." The configuration used is an IPsec VPN employing IKEv2, designed to route internet traffic from LAN-side terminals via ZIA.
A significant feature of this configuration example is the redundancy of two tunnel systems, with Tokyo IV designated as the main and Tokyo V as the backup. The main connection gateway is 165.225.110.24, and the backup is 167.103.8.130. Both utilize global IP addresses obtained by resolving the VPN Host Name of the target location via DNS. The default route is directed to the main Tunnel 6, and the system is configured to automatically switch to Tunnel 7 if an anomaly is detected by Keepalive monitoring.
The IPsec VPN parameters are based on the recommended values from the official ZIA website. IKE SA uses IKEv2, Pre-Shared Key method, DH Group is 1024-bit MODP Group, encryption is AES256-CBC, authentication is SHA-HMAC, IKE SA lifetime is 86400 seconds, NAT traversal is enabled, and DPD is set to detect failure after 5 consecutive failures at 20-second intervals. CHILD SA uses tunnel mode, ESP, PFS disabled, AES256-CBC and SHA-HMAC, IPsec SA lifetime is 28800 seconds, with rekeying set to occur when 90% of the lifetime is reached.
On the Yamaha router side, LAN1 is configured with 192.168.112.1/24, combining WAN connection using a PPPoE line with NAT, DHCP, DNS, and NTP settings. For IPsec Tunnel 6 and Tunnel 7, the User-FQDN and Pre-Shared Key configured on the ZIA side are registered respectively. Traffic destined for the ZIA Gateway is routed directly to pp 1 to avoid hindering tunnel establishment. Note that if using ZIA's SSL inspection feature, the root certificate distributed from the ZIA administration screen must be installed on the client devices. Connection verification is performed using the "show ipsec sa" and "show status tunnel" commands, and if the status is as expected, it is determined that the IPsec VPN with ZIA has been established.