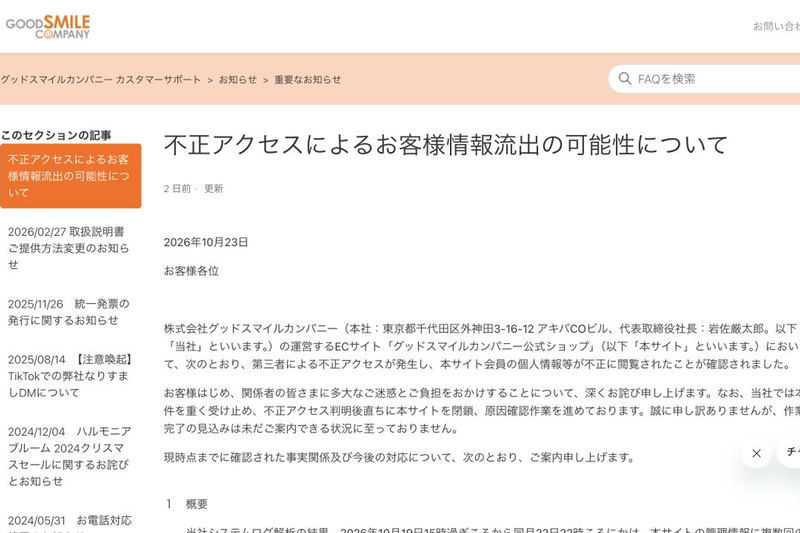
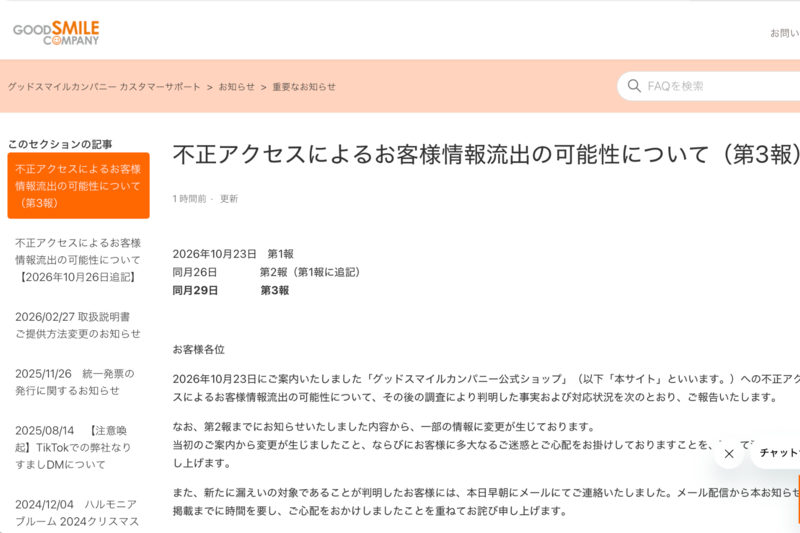
Good Smile Company announced its third report on October 29 regarding unauthorized access to its official online shop. It states that up to 2,800 users may have had their full credit card numbers, security codes, and other information leaked.
Users who may have had all their information leaked are those who potentially entered information on the shop's card payment page between 1:55 PM on October 21 and 7:00 AM on October 23. The affected information includes cardholder name, 16-digit card number, expiration date, and security code. This group includes 384 people who completed card payments, as well as those who attempted payment, those who added items to their cart, and 185 people who changed their card information after making a reservation.
The company's system does not retain operational records, making it impossible to individually identify those who attempted payment or added items to their cart. While it is believed that users who only added items to their cart and did not proceed to payment have not had their card information leaked, the company states it is contacting all potentially affected individuals. Those who attempted to change their card information but did not complete the process may also be affected. Since these individuals cannot be identified, the company is urging anyone who has a recollection of such an action to check their card statements.
For some registered card information, the last four digits of the card number and the expiration date may have been leaked. The number of affected cards, excluding duplicates, is 402,466. Cardholder names, security codes, and member information linked to the cards have not been leaked.
Regarding order information, data for 7,673 people who placed orders between approximately 10:20 PM and 11:00 PM on October 22 is within the scope of potential viewing. While 202 orders were confirmed to have been illicitly viewed, the company could not fully identify which specific order information was viewed, thus it is treating all 7,673 individuals as potentially affected. This potentially includes names, addresses, phone numbers, email addresses, order contents, amounts, and payment methods.