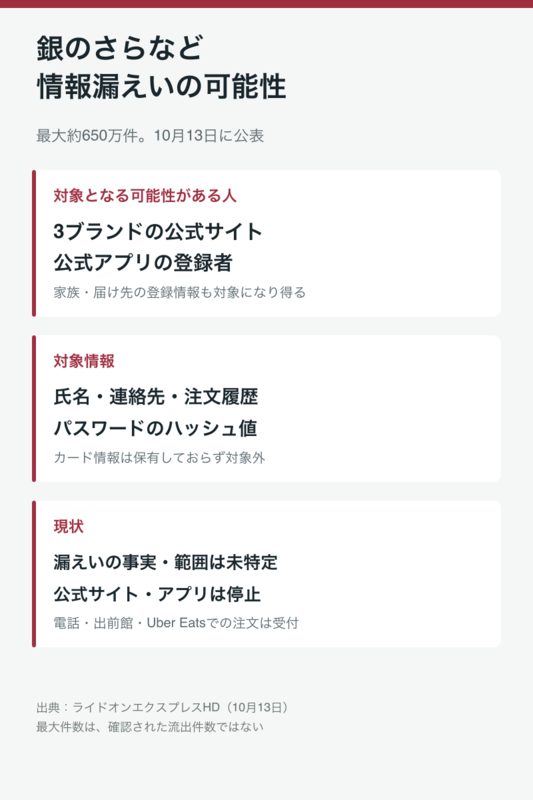
Ride On Express Holdings announced on October 13 that up to approximately 6.5 million records of information registered in official apps such as "Ginsara," "Kamatora," and "Sushi Joto" may have been leaked.
Potentially leaked items include names, addresses, phone numbers, email addresses, genders, dates of birth, order histories, and Deli Point member IDs. Regarding passwords, processed hash values, rather than plaintext strings, may be among the compromised data.
If family names and birthdays were entered during registration, or if recipient names, addresses, and phone numbers were registered when placing an order, those details may also be affected. Conversely, individuals who placed orders solely through Demae-can, Uber Eats, or by phone are not impacted. The company also stated that credit card information is not included in the leaked data, as it does not retain such information.
As of the announcement, no secondary damage resulting from the unauthorized use of the leaked information has been confirmed. The company urges users not to respond to suspicious communications or emails requesting password input, and to avoid opening any links.
Made with AI