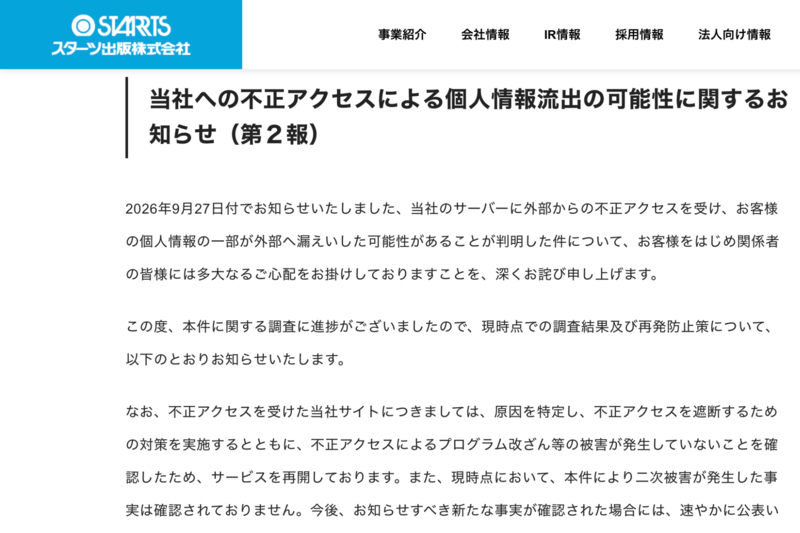
It has been revealed that up to 442,779 individuals may have had their personal information viewed in connection with the unauthorized access incident involving "OZmall." Starts Publishing announced this on October 1st, via its second report concerning the unauthorized access to its servers. The affected individuals include OZmall members and some former members, with the possibility that email addresses, and for some, names and prefectures of residence, were viewed.
The unauthorized access was discovered on September 26th when the company's system department detected a large volume of access originating from overseas. They temporarily suspended the relevant pages and implemented countermeasures, with subsequent investigation confirming the possibility of personal information being viewed. A report was submitted to the Personal Information Protection Commission on September 28th.
While the first report stated "up to 447,610 individuals," this number has been revised to a maximum of 442,779 individuals as the investigation progressed. It was also revealed that information belonging to some former members, which was retained for a certain period for transaction history management, is also included among the affected data.
There is no evidence that detailed addresses, including phone numbers and street numbers, were viewed. As credit card information is handled by an external payment system, there is no possibility of it being leaked. No secondary damage has been confirmed at this time.
The company has implemented countermeasures against the vulnerability that caused the incident and has resumed its services. They are sequentially contacting potentially affected users via email and urging them to be cautious about opening links or attachments in suspicious emails impersonating the company or other legitimate businesses.