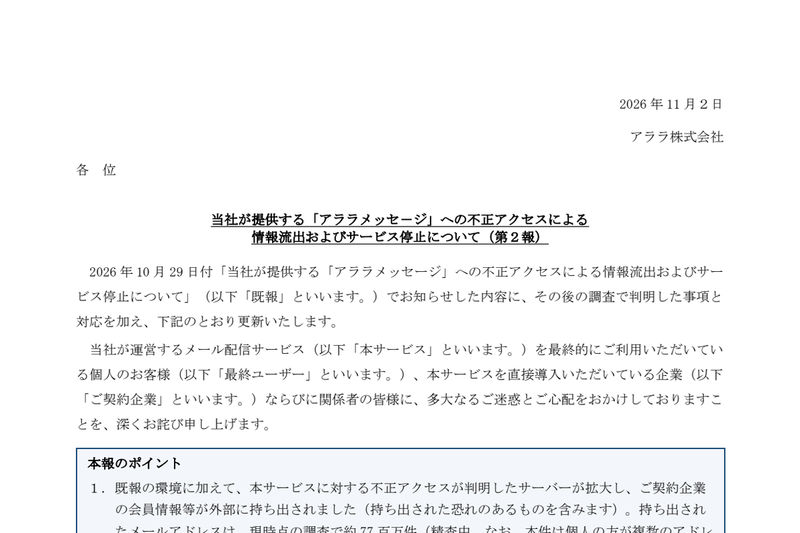
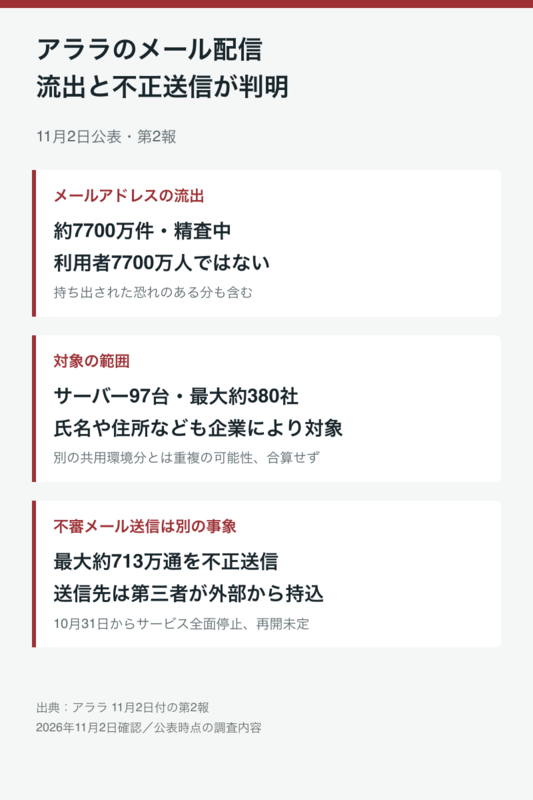
On November 2nd, Arara announced that approximately 77 million email addresses were exfiltrated due to unauthorized access to its email delivery service, "Arara Message." This figure includes potentially exfiltrated data and is currently under scrutiny. All service provision was halted on October 31st, with the restart date yet to be determined.
Arara Message is a service that enables businesses to send emails to their customers. A third party infiltrated numerous servers via the service's servers and exfiltrated database contents. The targets were 97 servers used by client companies, with an estimated maximum of approximately 380 companies affected.
In addition to email addresses, the leaked information includes names, genders, dates of birth, phone numbers, membership IDs, and addresses registered by client companies. The specific items vary by company. The company's service does not store credit card numbers.
The damage to the shared environment, initially reported on October 29th, has also expanded. The number of affected companies is 61, and the count of email addresses, excluding duplicates, has been revised to 3,386,187. Among these, it was also discovered that customer data, including names and company names, totaling up to 411,827 records, was exfiltrated from five companies.
The service was also exploited for sending suspicious emails. Between October 28th and 30th, approximately 7.13 million emails impersonating credit card companies were sent from two environments. The recipients were addresses brought in externally by a third party. The sender was "news@arara.com," and the subject lines included "Request for usage confirmation" and "Request for statement confirmation."
Arara has invalidated fraudulently used authentication information and blocked communications. The company continues to investigate, stating that the cause is related to system environment issues in addition to web server vulnerabilities.
Made with AI