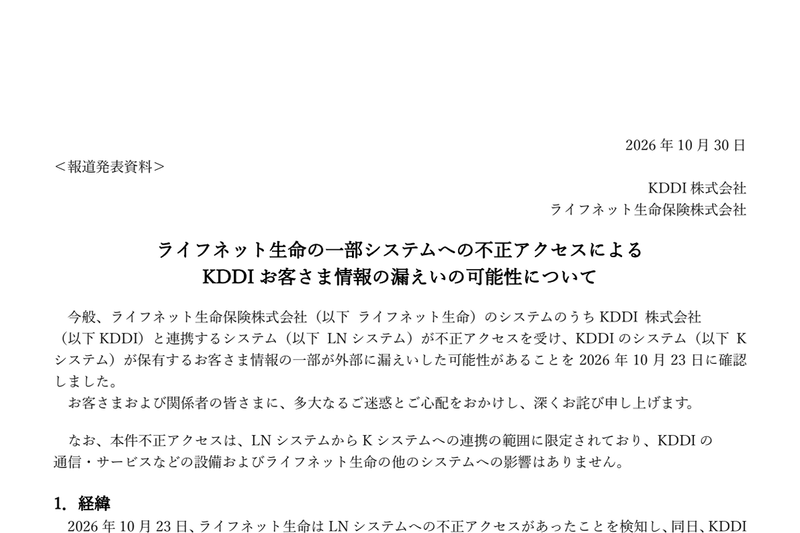
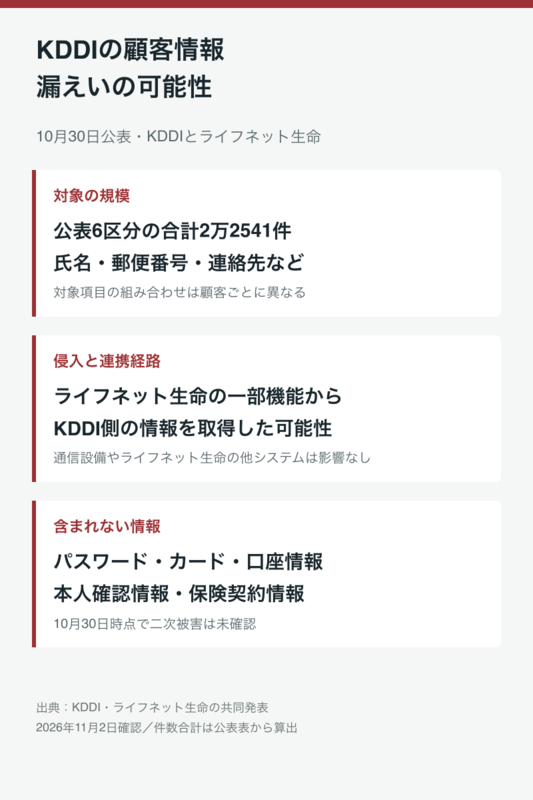
KDDI and Lifenet Insurance announced on October 30 that KDDI customer information may have been leaked externally due to unauthorized access to a portion of Lifenet Insurance's systems. The total number of potentially compromised records across various categories amounts to 22,541.
The unauthorized access targeted the part of Lifenet Insurance's systems that integrates with KDDI. It is suspected that a third party exploited a vulnerability in some functions to obtain information residing on KDDI's systems.
The affected data points include names, postal codes, phone numbers, email addresses, and member identifiers. The specific combination of potentially leaked items varies per customer, with 807 cases involving only the member identifier. In some instances, gender and date of birth were also compromised.
Lifenet Insurance detected the unauthorized access on October 23 and promptly implemented protective measures. KDDI, on the following day, October 24, blocked the access route from Lifenet Insurance. As a result, some functions of "au Life Insurance" (au no Seimei Hoken), including application acceptance, are currently undergoing maintenance.
As of the October 30 announcement, no secondary damages, such as unauthorized use of the compromised information, have been confirmed.
Made with AI