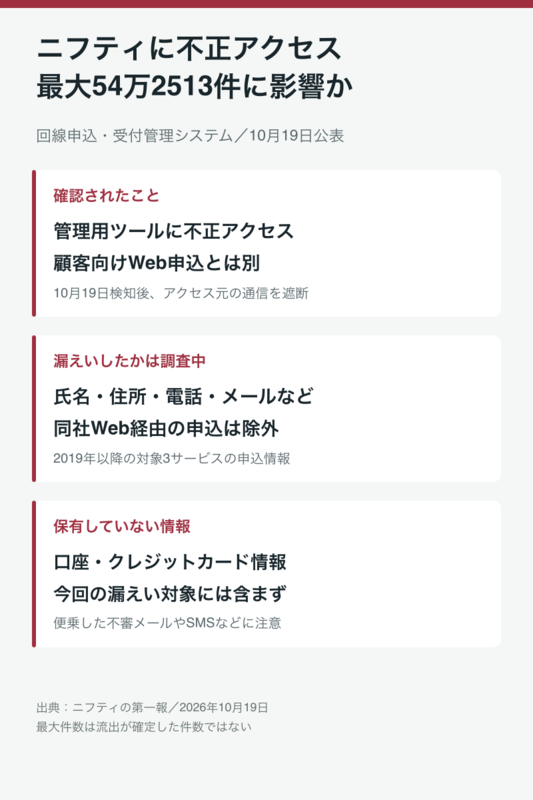
Nifty announced on October 19th that it has confirmed unauthorized external access to its line application and reception management system. There is a possibility of a leak of up to 542,513 application records, and the company is investigating the incident with external specialized organizations. The specific information that may have been leaked is currently under investigation.
The affected system is a management tool used by the company to register information. The unauthorized access was confirmed around 10:20 AM on October 19th, and communication from the access source was immediately blocked upon detection.
Information of users who applied for "@nifty光", "@nifty MAX光", or "@nifty auひかりプラス" since 2019 may be affected. The potentially compromised items include member ID, name, gender, date of birth, address, phone number, and email address. Account and credit card information are not held within the system in question and are therefore not included in this potential leak.
The company has implemented provisional measures to prevent further damage and is proceeding with a detailed investigation and reporting procedures to the Personal Information Protection Commission. Based on the investigation results, Nifty plans to strengthen its security measures and monitoring systems, stating that it will make public any new facts or response policies as soon as they are determined.
Made with AI