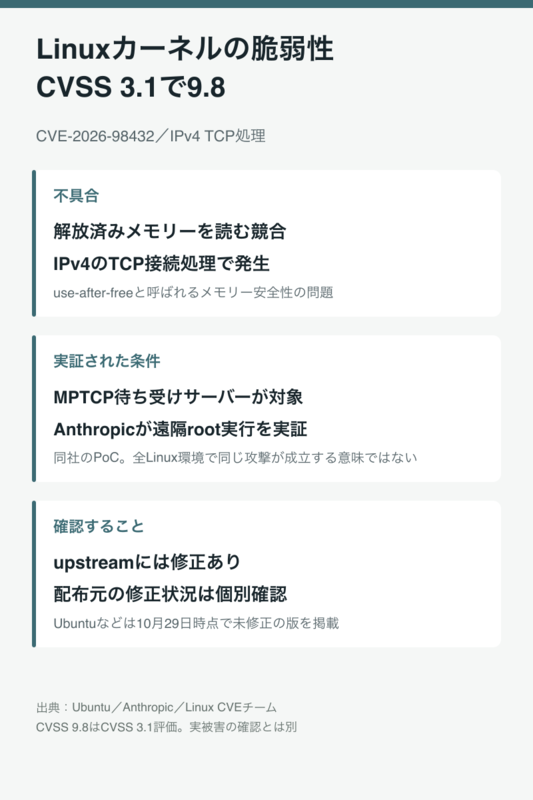
Anthropic announced on October 27th that it successfully demonstrated an attack exploiting the Linux kernel vulnerability 'CVE-2026-98432' to remotely execute commands with administrative privileges. The vulnerability is rated 9.8 out of a maximum of 10 for severity.
The issue lies within the Linux kernel's IPv4 communication processing. It's a 'use-after-free (UAF)' flaw, where already freed memory is referenced during TCP connection handling. This vulnerability can be exploited over the network without requiring authentication or user interaction.
Anthropic's demonstration targeted a listening server utilizing 'MPTCP' (Multipath TCP), which uses multiple communication paths. They reported that by using AI-generated attack code, they were able to remotely execute commands with root privileges without authentication.
The CVE team, responsible for managing Linux kernel vulnerability information, publicly disclosed the issue on October 15th, and a fix has since been incorporated into stable versions. However, Ubuntu's update information from October 29th indicates that multiple versions are still either undergoing remediation or remain vulnerable.
Server administrators must check the patch status released by their respective Linux distributions and apply the necessary updates.
Made with AI