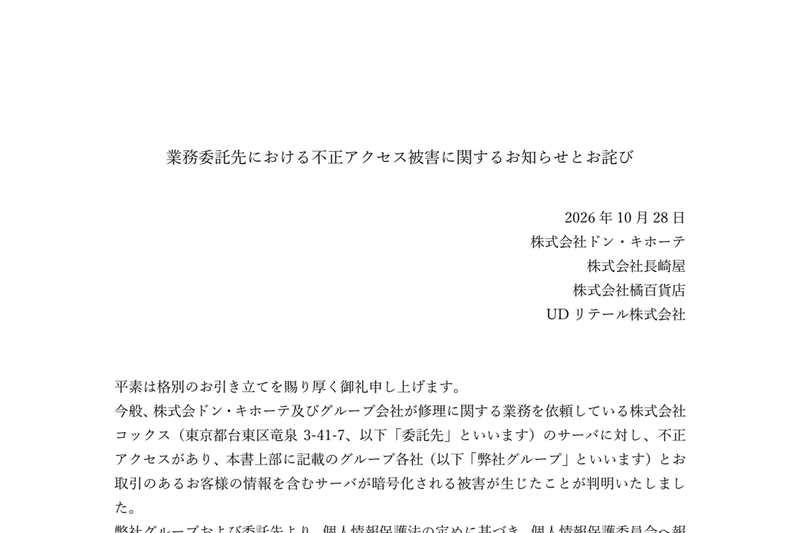
Don Quijote, Nagasakaya, Tachibana Department Store, and UD Retail announced on October 28th that customer information may have been leaked due to unauthorized access to a watch repair contractor. The contractor's server was encrypted by ransomware. While no actual data leak has been confirmed at this time, the companies state that the possibility cannot be completely ruled out.
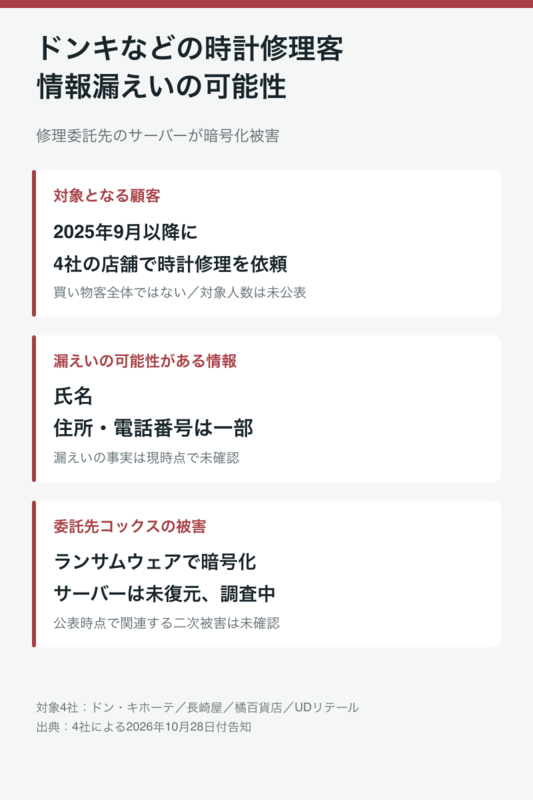
The affected customers are those who requested watch repairs at the group stores of the four companies after September 2025. The potentially leaked information includes names, and some addresses and phone numbers. The number of affected customers and data records has not been disclosed.
The server attacked belongs to Cox, which undertakes repair services. The company detected the possibility of a cyberattack on September 15th and confirmed that the server was encrypted and inaccessible. They reportedly blocked external connections and reported the incident to Don Quijote on September 25th.
The contractor is currently conducting an investigation with a specialized institution, but the encrypted server has not yet been restored.
Made with AI