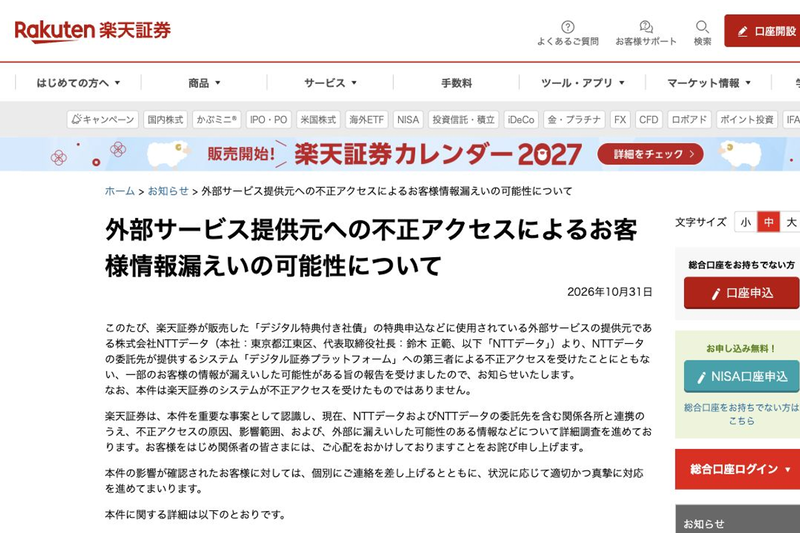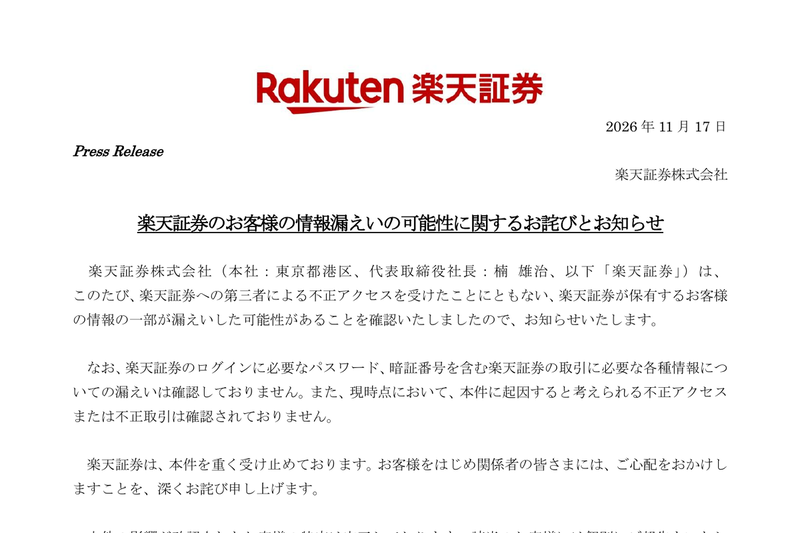
Rakuten Securities announced on November 17th that its internal test environment was subjected to unauthorized access, potentially leading to a customer information leak. The breach affects two categories: approximately 11.25 million accounts, limited to login IDs and similar information, and approximately 4.47 million accounts, which also include names, addresses, and financial asset information. A company spokesperson explained to IT journalist Kenta Yamaguchi that there is no overlap between the two categories, and the total, including former customers, amounts to a maximum of approximately 15.72 million accounts.
According to the spokesperson's response reported by Kenta Yamaguchi on Yahoo! News Expert on November 18th, the test environment typically used dummy data. However, due to an internal system update, it became necessary to verify operations using production environment data. The company explained that the unauthorized access occurred during the period when actual customer data was present in the test environment.
Rakuten Securities detected suspicious unauthorized access on November 16th and immediately blocked access to the affected area. Subsequent investigation revealed that information may have been leaked externally on November 11th.
For the approximately 11.25 million accounts, the affected data includes branch codes, customer codes, and securities account login IDs. For the approximately 4.47 million accounts, in addition to the above, the leaked information also includes birth dates, phone numbers, email addresses, employers, bank account details for withdrawals, declared annual income, financial assets, and asset holdings.
Rakuten Securities stated that it has not confirmed any leaks of login passwords or transaction PINs, nor has it identified any unauthorized logins or transactions stemming from this incident. The company is individually notifying affected individuals, urging them to be wary of phone calls or emails impersonating Rakuten Securities, and encouraging the use of passkeys.