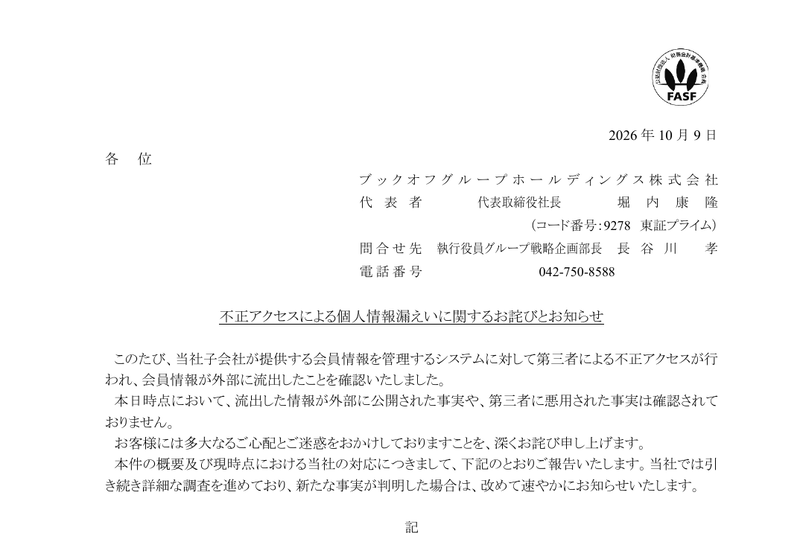
Bookoff Group Holdings announced on October 9 the potential leak of member data due to unauthorized access to a subsidiary's member management system. Up to approximately 6.43 million member data records are affected.
The affected member data may include names, dates of birth, genders, email addresses, phone numbers, addresses, point card numbers, member IDs, and potentially password hash values.
The system in question does not store payment information such as credit card details, so payment information is not included in the breach. The actual number of affected individuals and the full scope of the compromised information are currently under investigation, and no alteration of member information has been confirmed.
The company has contained the unauthorized access route and blocked communication from the attack source. As of now, it states that no external publication of information or misuse by third parties has been confirmed.