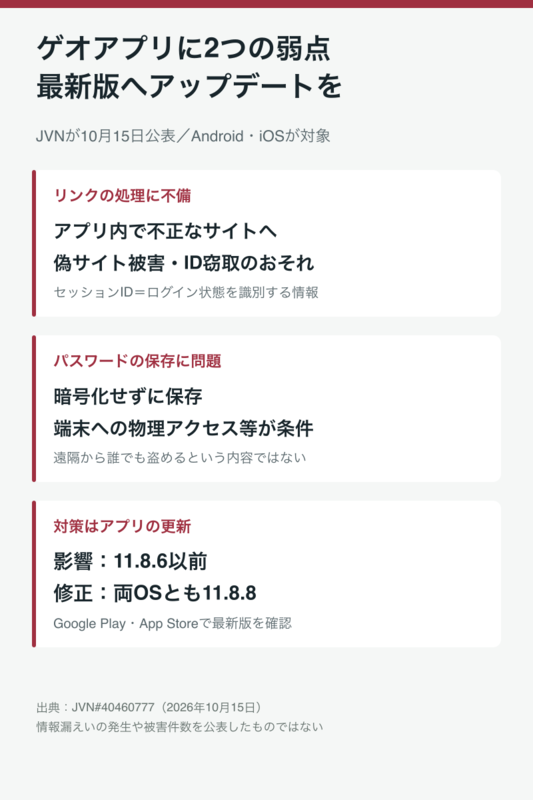
JVN, a provider of vulnerability information, announced on October 15th that versions 11.8.6 and earlier of the smartphone application 'Geo App' for Android and iOS have a vulnerability. Users are being urged to update.
The first vulnerability (CVE-2026-96614) concerns how links that launch the app are processed. If exploited, it could lead to fake websites being displayed within the app, potentially resulting in phishing scams.
The second vulnerability (CVE-2026-105271) involves storing important information without encryption, which could allow user passwords to be stolen. However, exploiting this vulnerability requires physical access to the device or certain permissions, meaning not just anyone can steal passwords.
The recommended countermeasure is to update the Geo App to version 11.8.8 or later. Android users can apply the latest version from Google Play, and iPhone users can do so from the App Store.
Made with AI