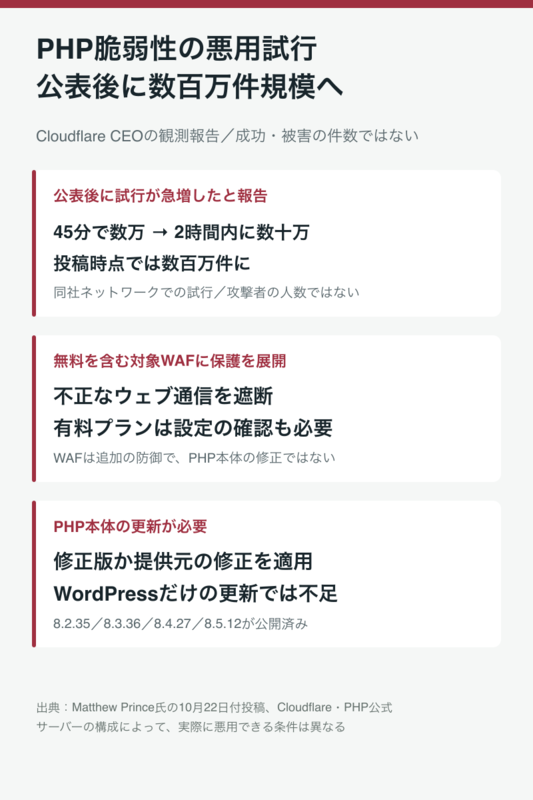
Cloudflare CEO Matthew Prince reported on his official X account around 10:25 AM on October 22nd that traffic attempting to exploit the PHP vulnerability "php2shell" was increasing across the company's network. Attempts, which numbered in the thousands in the 10 hours prior to the public announcement, jumped to tens of thousands within 45 minutes of the announcement, hundreds of thousands within 2 hours, and had reached millions by the time of his post.
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now. — Matthew Prince 🌥 (@eastdakota) October 22, 2026
In an official blog post dated October 21st, Cloudflare explained that it had deployed Web Application Firewall (WAF) protection, which prevents malicious traffic to websites, to eligible environments, including free plans.
However, WAF is an additional layer of defense and not a substitute for fixing the PHP core itself. The PHP development team released patched versions 8.2.35, 8.3.36, 8.4.27, and 8.5.12 on October 21st, and strongly recommends immediate updates.
Made with AI