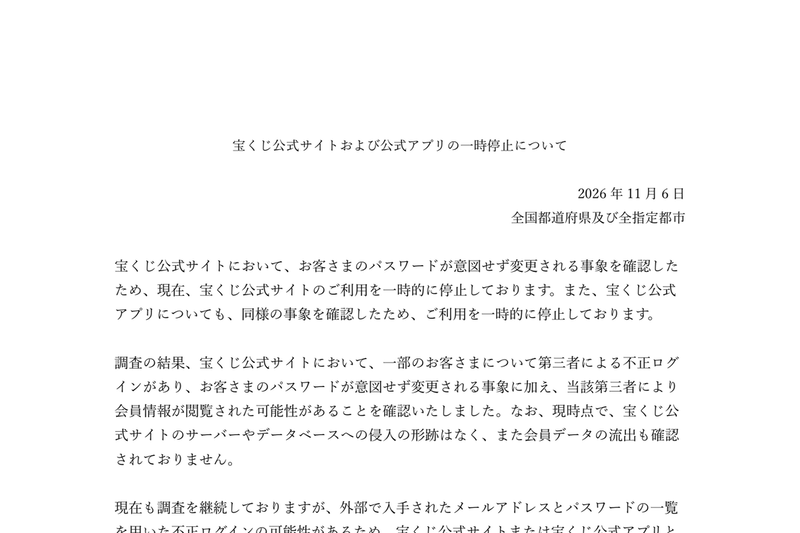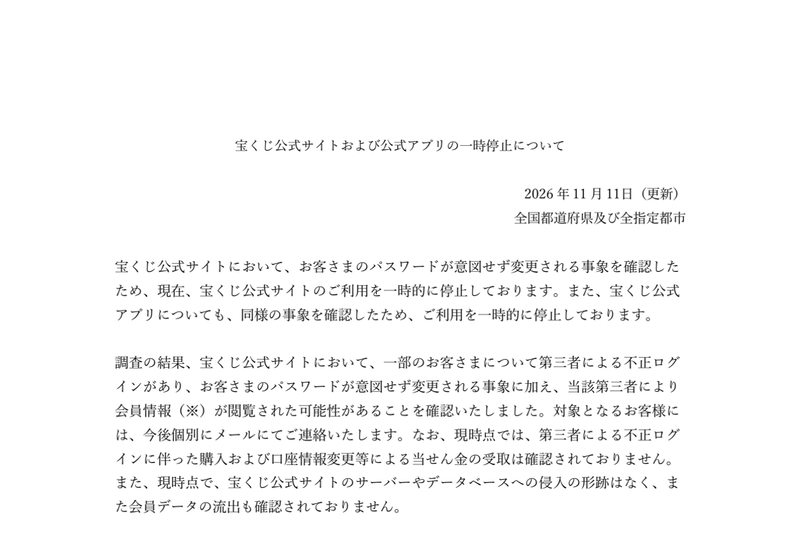
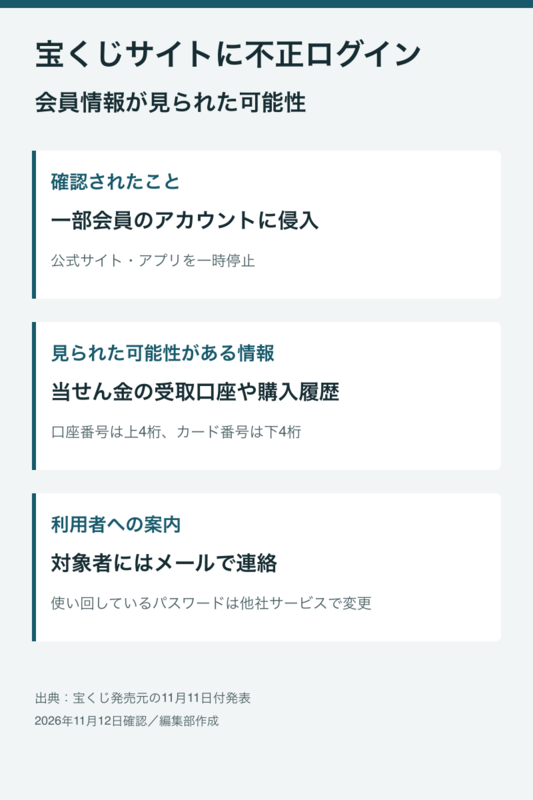
On November 11, prefectures and designated cities nationwide, the distributors of the lottery, announced that a third party may have illicitly accessed some member accounts on the Lottery Official Website, potentially viewing member information. The official website and app have been temporarily suspended after incidents of passwords being unintentionally changed were confirmed. Affected individuals will be contacted individually via email.
Potentially viewed information includes names, addresses, phone numbers, email addresses, as well as the type, amount, and win/loss status of purchased lottery tickets. For payout bank accounts, the financial institution name, the first four digits of the account number, and the account holder's name are targeted. For credit card numbers, only the last four digits are affected. The total number of affected cases has not been disclosed.
There is a possibility that this was a 'credential stuffing attack,' where attackers attempt to log in using combinations of email addresses and passwords obtained from external data breaches. Users who are reusing the same password combinations across multiple services are urged to change their passwords for those other services.
Made with AI