On November 6, the Ministry of Internal Affairs and Communications (MIC) issued an alert to businesses operating websites and smartphone applications, urging them to thoroughly implement measures against unauthorized access. The ministry particularly emphasized caution for businesses handling personal information. This move follows a similar communication from the National Center of Incident Readiness and Strategy for Cybersecurity (NISC) under the Cabinet Secretariat, with the MIC now disseminating the same message to businesses under its jurisdiction and related organizations.
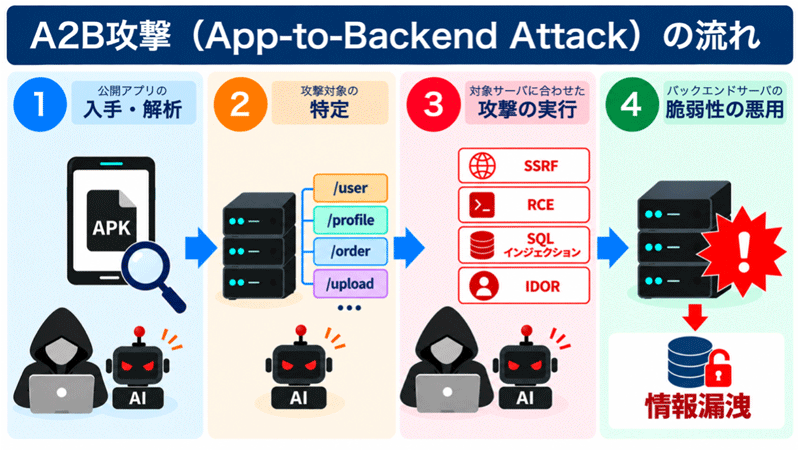
According to the MIC, multiple data breaches caused by unauthorized access were attributed to a lack of basic measures, such as insufficient countermeasures during app development, website misconfigurations, and failure to address known vulnerabilities. The ministry also suggested the possibility that attackers gained entry by combining multiple weaknesses that, individually, were considered relatively low risk.
The MIC also mentioned the possibility of attackers using AI for reconnaissance and intrusion. It believes that as attacks become easier to scale, businesses of all sizes could become targets.
The MIC urged businesses to fix known weaknesses and misconfigurations, and to continue security diagnostics and monitoring even after their services are launched. It also advised incorporating countermeasures from the design and development stages, and if development and operations are outsourced, to inspect the measures taken by the vendor. The ministry encouraged management to take the lead in reviewing the entire scope of operations, including both in-house managed components and outsourced areas.