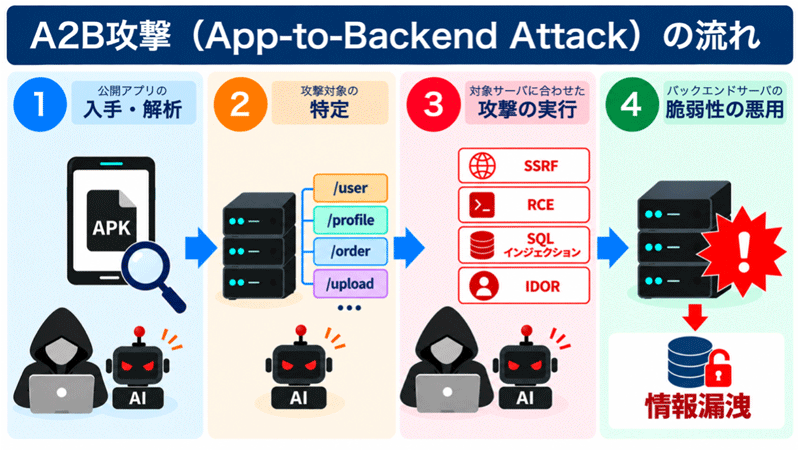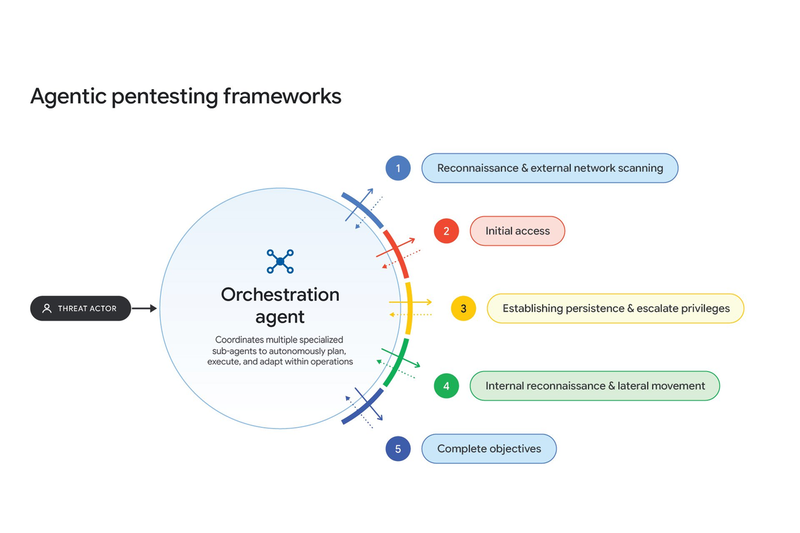
Google's Threat Analysis Group (TAG) and its subsidiary Mandiant announced on November 17 that they have confirmed a mechanism that uses AI agents to automate the entire process from discovering software vulnerabilities to executing attack code. AI tools were also found to be used in some stages of actual intrusion activities, such as reconnaissance.
The research team discovered an attacker-controlled server accessible from the outside. This server was equipped with a tool capable of comparing code before and after Web application patches to identify potential weaknesses, creating exploit code, and executing it without human intervention.
In another case, a tool linking multiple AIs was used for intrusion activities targeting areas such as the U.S. aerospace sector. In Asia, there were also reports of modified publicly available penetration testing tools being used to conduct reconnaissance and vulnerability scanning against various organizations.
What is particularly problematic is that when a patch is released, the differences provide clues for attackers to find weaknesses. On the other hand, Google states that while automation increases the speed of attacks, it also leaves distinctive communication patterns and unique code-level traces, which can sometimes lead to detection.
Made with AI