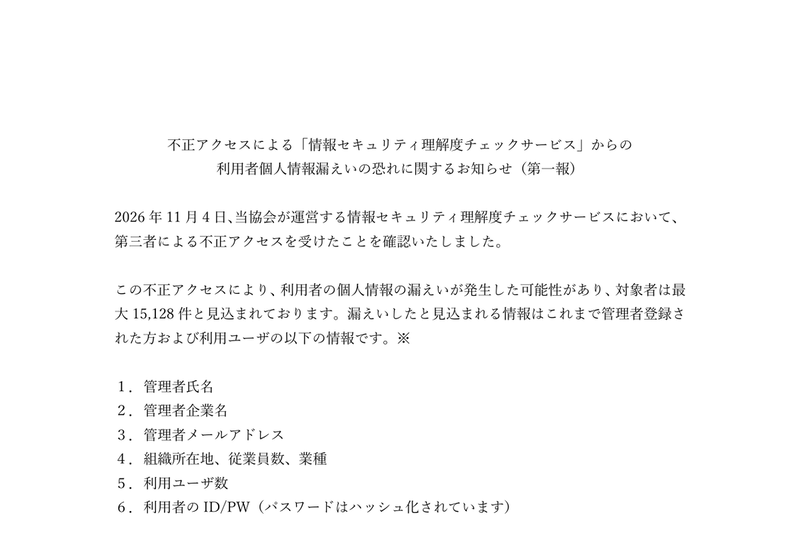
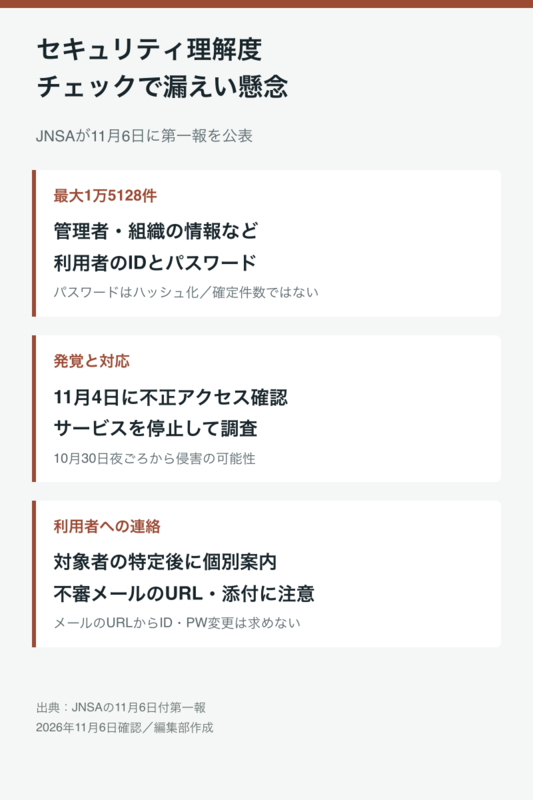
The Japan Network Security Association (JNSA) announced on November 6th that its "Information Security Comprehension Check Service" suffered unauthorized access, potentially leading to the leakage of user personal information. Up to 15,128 records could be affected. The service has been suspended for investigation.
The service allows organizational administrators to register employees and staff, have them take information security quizzes, and analyze the results. Participants other than administrators can be managed using "participant IDs" instead of personal names.
Potentially leaked information includes administrators' names, company names, and email addresses; organizational addresses, number of employees, and industry; number of users; and users' IDs and passwords, with passwords being hashed.
JNSA confirmed the unauthorized access on November 4th. It has been determined that the unauthorized access likely occurred around the evening of October 30th, and they are currently investigating the intrusion path and scope of impact with external specialists.
JNSA is urging caution against emails impersonating the association or related organizations, and advises against opening suspicious email links or attachments. The association states that it will never request users to enter or change IDs or passwords via a URL in an email body.
Made with AI